Read-only by default
Aurykle does not need permission to administer connected identity systems.
Aurykle gives identity, platform, and security teams an independent, reviewable history of supported configuration across their identity providers. Auth0 and Amazon Cognito are available in the current beta.
Independent assurance for identity infrastructure
The change record, rebuilt
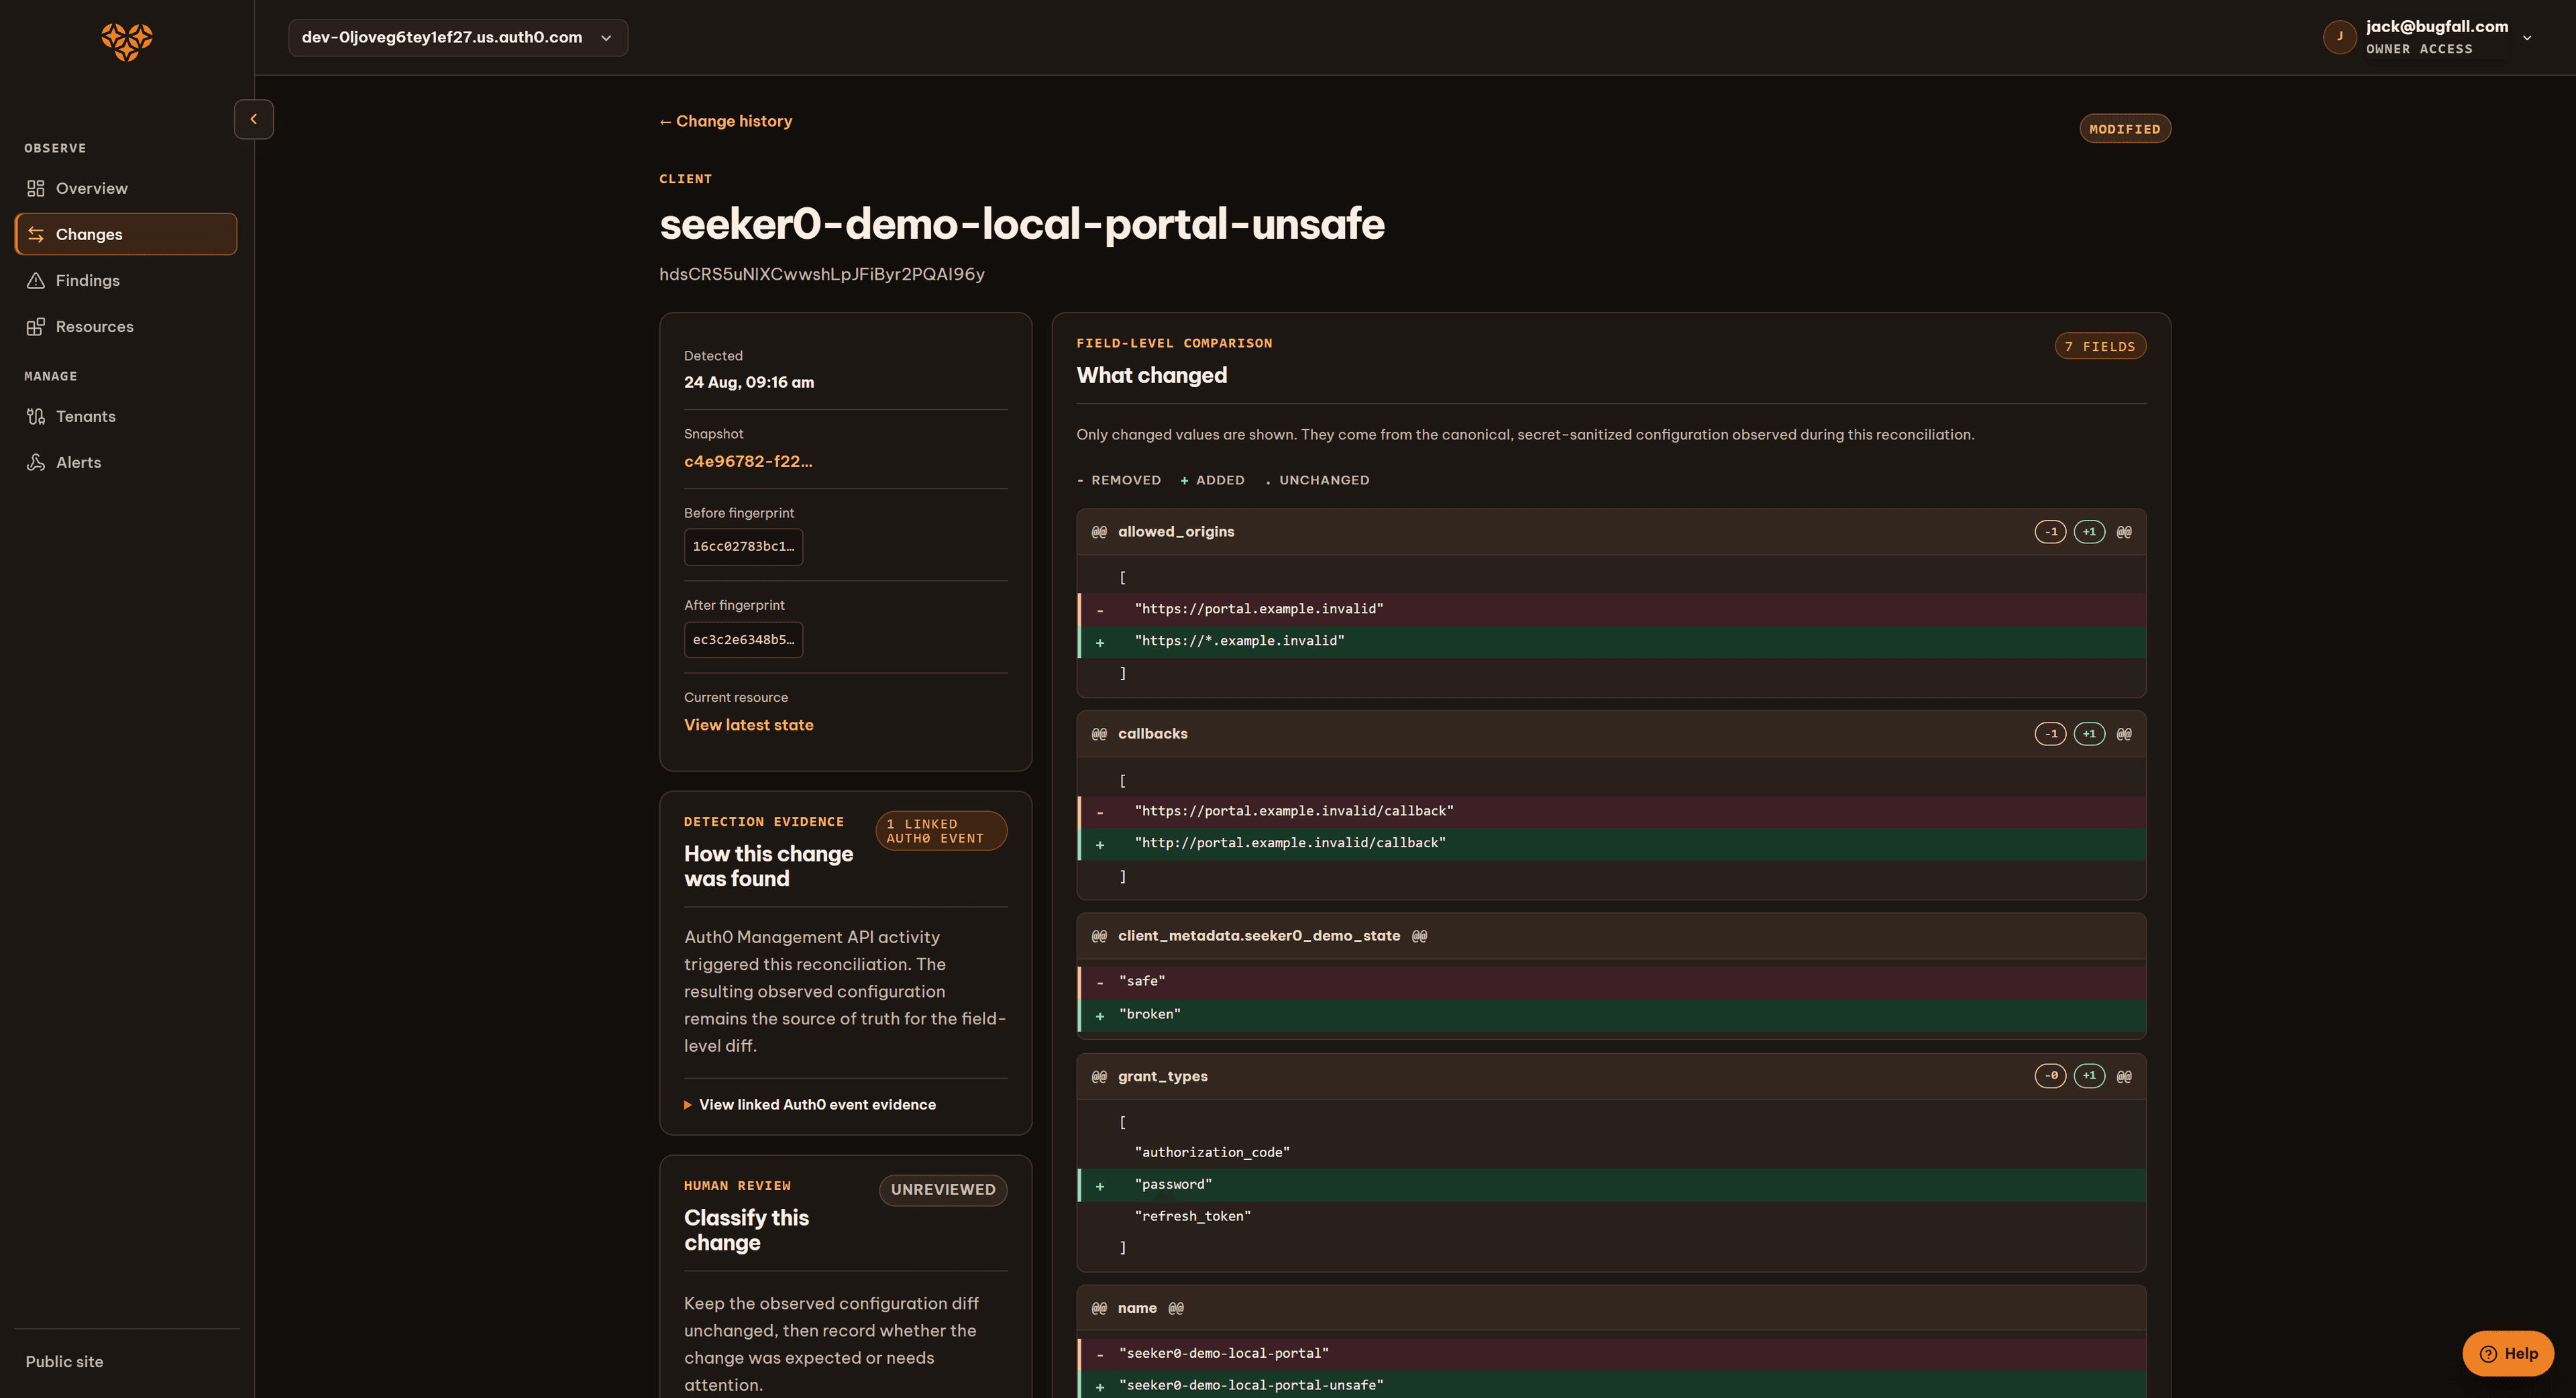
A notification that says something changed still leaves a team to reconstruct what happened. Aurykle keeps the affected resource, field-level difference, snapshot state, and review context in one deliberate record—whether the change came from Terraform, CDK, Bicep, Ansible, or a provider dashboard.
Explore the workflowBaseline your supported configuration with a dedicated read-only connection.
One record. All of the useful context.
Open findingReview the exact change against a complete snapshot, not an incomplete event.
A quieter way to operate
Connect each provider with the minimum read-only access and capture the supported resources your team needs to oversee.
Compare complete snapshots to isolate the resource and field that actually changed.
Keep an evidence-ready history for triage, handovers, incident response, and audit conversations.
Security by design
Aurykle is designed to observe your identity configuration, not administer it.
Aurykle does not need permission to administer connected identity systems.
Connection credentials are encrypted in Vault and never returned to the browser.
Sensitive configuration is excluded and only complete snapshots are compared.
Before you connect
No. Aurykle uses dedicated, provider-appropriate read-only connections to observe supported configuration. It does not make changes to connected tenants or directories.
Free private beta
We are onboarding a small number of identity, platform, and security teams directly. There is no charge during beta. Features, coverage, limits, and availability may change.
Request private beta